10 Cyber Security Books That Separate Experts from Amateurs
Trusted recommendations from Katie Paxtonfear, Ben Goldacre, and Steve Wozniak highlight crucial Cyber Security Books for all levels
Updated on June 28, 2025·We may earn commissions for purchases made via this page
10 of 10 books have Kindle versions
We're launchingLaunching on Product Hunt today 🎉We just launchedJust launched on Product Hunt 🎉
Modelpeers, from the BookAuthority teamFrom the BookAuthority team: Modelpeers, a free way to follow AI models and agents like you follow people. We'd love your support.
What if you could see the unseen threats lurking in the digital shadows? Cyber security isn't just a buzzword—it's the frontline defense for our most sensitive data and systems. With cyber attacks evolving rapidly, understanding these hidden dangers is crucial whether you're a seasoned professional or just starting out.
Experts like Katie Paxtonfear, a cybersecurity researcher and lecturer, have praised Practical IoT Hacking for its hands-on approach to the fast-growing world of connected devices. Meanwhile, Ben Goldacre, an Oxford academic, highlights The Art of Invisibility for unveiling the mechanics behind social engineering attacks, making privacy concerns tangible and actionable. Steve Wozniak, cofounder of Apple, emphasizes the importance of practical education in digital privacy through these insightful works.
While these expert-curated books provide proven frameworks, readers seeking content tailored to their specific experience level, interest in IoT or malware, or career goals might consider creating a personalized Cyber Security book that builds on these insights and addresses your unique challenges.
Best for IoT security professionals and researchers
Kindle version available
Katie Paxtonfear, a lecturer and noted infosec researcher, highlights the value of this book by calling it a "great modern book on IoT hacking that came out just recently." Her extensive background in cybersecurity research gives weight to her recommendation, especially as IoT security continues to grow in importance. She found Practical IoT Hacking to be a timely resource that helped sharpen her understanding of modern IoT threats. Her endorsement signals to you that this book offers grounded, current insights essential for anyone serious about securing connected devices. Following her, Craig Smith, author of the Car Hacker's Handbook, praises it as an essential addition to any hardware hacker's toolkit, underscoring its practical utility for hands-on professionals.
Fotios Chantzis, Ioannis Stais, Paulino Calderon, Evangelos Deirmentzoglou, Beau Woods(you?)·
About the Author
Fotios (Fotis) Chantzis is laying the foundation for a safe and secure Artificial General Intelligence (AGI) at OpenAI. Previously, he worked as a principal information security engineer at Mayo Clinic, where he managed and conducted technical security assessments on medical devices, clinical support systems, and critical healthcare infrastructure. He has been a member of the core Nmap development team since 2009, when he wrote Ncrack under the mentorship of Gordon “Fyodor” Lyon, the original author of Nmap, during the Google Summer of Code. He later worked as a mentor for the Nmap project during the Google Summer of Code 2016 and 2017 and has authored a video course about Nmap. His research on network security includes exploiting the TCP Persist Timer and inventing a stealthy port scanning attack by abusing XMPP. Fotis has presented at notable security conferences, including DEF CON.
When Fotios Chantzis and his co-authors first crafted this guide, their combined expertise in IoT and network security shaped a practical manual that goes beyond theory to hands-on hacking techniques. You’ll learn detailed methods for testing IoT devices, including VLAN hopping, MQTT authentication cracking, and firmware reverse engineering. The book dives deep into hardware and radio hacking, showing you how to expose vulnerabilities in embedded systems and RFID technologies. Whether you’re an IT security professional, researcher, or hobbyist, you’ll gain a clear framework for assessing risks and implementing defenses across IoT layers. Chapters on crafting specific attacks like mDNS poisoning and NFC fuzzing provide concrete skills you can apply immediately.
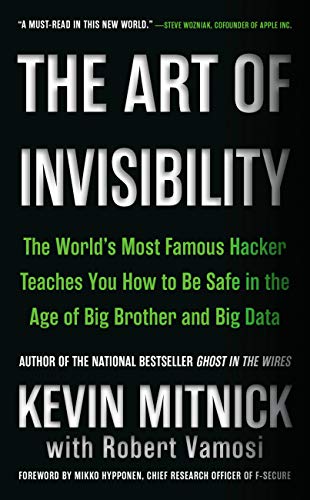
Ben Goldacre, a doctor and academic at Oxford’s Centre for Evidence-Based Medicine, highlights how this book reveals the mechanics behind coordinated social engineering attacks, noting it makes complex hacking techniques accessible through clear writing. His appreciation stems from the book's ability to demystify cyber threats, providing a roadmap to better protecting yourself online. This perspective aligns with Baptiste Robert, an ethical hacker, who endorses the book’s expertise in practical cyber defense, strengthening the case for its value in your digital security toolkit.
“Oh wow Twitter say this huge hack was done through a coordinated social engineering attack. Hugely recommend Kevin Mitnick's book on this: The Art of Deception. Also a great example of (openly disclosed) ghost writing making a technical topic very readable” (from X)
Kevin Mitnick has been the subject of countless profiles published and broadcast throughout the world. Mitnick's leading penetration-testing team is highly respected and sought after for its security services by the world's top corporations and governments. The company he founded, Mitnick Security Consulting LLC, has clients that include dozens from the Fortune 500 and many nations across the globe. Mitnick is the bestselling author of The Art of Invisibility, Ghost in the Wires, The Art of Intrusion, and The Art of Deception. He lives in Las Vegas and travels the world as the top keynote speaker on cybersecurity.
Kevin Mitnick, once the FBI's most wanted hacker, wrote this book to share the insights he gained from years of both exploiting and defending digital systems. You learn practical methods to protect your identity online, from securing passwords to avoiding Wi-Fi pitfalls, all illustrated with real-life hacking stories that reveal how easily your privacy can be invaded. The book is designed for anyone concerned about online privacy, especially those wanting to grasp how their data is tracked and how to counteract it. It’s a straightforward guide that arms you with tools to stay invisible in an era dominated by big data and surveillance.
This AI-created book on cyber defense is tailored to your experience and goals, ensuring the content matches your specific interests and skill level. By sharing your background and focus areas, you receive a guide that walks you through cyber security concepts and practices most relevant to you. This personalized approach helps you build expertise efficiently, cutting through generic advice and honing in on what truly matters for your learning journey.
TailoredRead AI creates personalized nonfiction books that adapt to your unique background, goals, and interests. Instead of reading generic content, you get a custom book written specifically for your profession, experience level, and learning objectives. Whether you're a beginner looking for fundamentals or an expert seeking advanced insights, TailoredRead crafts a book that speaks directly to you. Learn more.
This tailored Cyber Security Mastery Blueprint explores the essential skills and knowledge you need to confidently navigate the complex world of cyber defense. It covers foundational concepts such as threat identification, network security, and malware analysis, while examining advanced topics including penetration testing and incident response. This personalized guide matches your background and interests, focusing on the areas most relevant to your goals, whether you aim to strengthen your technical expertise or understand emerging threats. By synthesizing expert knowledge into a clear, tailored pathway, it reveals how to build practical skills and deepen your understanding of cyber security defenses effectively.
Alex Caceres, owner of Hyperion Gray and DARPA researcher, highlights the value of immersive, lab-focused learning for network security, citing penetration testing courses and resources like Georgia Weidman's work for deeper insight. His recommendation underscores the importance of hands-on experience in mastering complex cybersecurity techniques. Meanwhile, Help Net Security praises the book's clear, practical introduction to hacking, emphasizing its suitability for beginners. Together, their perspectives suggest this book is a solid foundation for anyone serious about developing real-world penetration testing skills.
“@gvgm3 @SecurityTube For networks I'd have to say hands down the OSCP is likely one of the best you're going to find. Fuck the cert, take the course, get down and dirty in the labs and break everything. I hear @georgiaweidman's book is good (Pen testing with Metasploit) but have not read it myself” (from X)
Georgia Weidman is a penetration tester and researcher, as well as the founder of Bulb Security, a security consulting firm. She presents at conferences around the world, including Black Hat, ShmooCon, and DerbyCon, and teaches classes on topics such as penetration testing, mobile hacking, and exploit development. She was awarded a DARPA Cyber Fast Track grant to continue her work in mobile device security.
Georgia Weidman's extensive experience as a penetration tester and security researcher led her to craft this hands-on guide, focusing on practical skills essential for aspiring hackers. You’ll gain concrete abilities like cracking passwords, testing web app vulnerabilities, and using tools such as Metasploit and Burp Suite through lab-based lessons that simulate real-world attacks. The book also dives into mobile hacking techniques, reflecting Weidman's specialized research in that area. If you want to understand each phase of a penetration test—from reconnaissance to post-exploitation—this book walks you through it thoroughly, making it especially useful for those new to cybersecurity who want a solid foundation in offensive security.
Best for cybersecurity beginners seeking practical skills
Kindle version available
Sam Grubb brings six years of cybersecurity consulting and teaching experience to this guide, currently serving as Cyber Defense Operations Manager at Centennial Bank. Holding the CISSP certification and a master's in military history, his expertise informs a practical approach to cybersecurity that makes the subject accessible to beginners and professionals alike. His passion for threat analysis and risk management shines through, making this book a solid foundation for anyone wanting to understand how cybersecurity really works.
Sam Grubb is a cybersecurity consultant for a managed service provider that works with a large variety of clients. He has six years of experience teaching cybersecurity to both adults and teenagers and holds several cybersecurity certifications, including the Certified Information Systems Security Professional (CISSP) certification. Sam currently works as the Cyber Defense Operations Manager at Centennial Bank. Previously, he’s worked as a Senior Cybersecurity Consultant at Edafio. He is an expert in security awareness, risk management, policy and compliance. His true passion lies in threat analysis and he is currently growing his threat detection and intelligence, incident response, and digital forensic skills. Sam has a Masters in Military History from Norwich University. He is an author of How Cybersecurity Really Works: A Hands-On Guide for Total Beginners, published by No Starch Press. He has also written for Arkansas Business Magazine and other publications. Sam has a passion for teaching and believes anyone can learn anything, given the right instruction.
When Sam Grubb decided to write this book, his extensive experience in cybersecurity consulting and teaching shaped a no-nonsense introduction to the field. You’ll gain a clear understanding of how attackers think and operate, along with practical skills like analyzing phishing emails, deploying encryption, and using command-line tools to enhance security. The book breaks down complex concepts such as malware and social engineering into approachable lessons, supported by real-world examples and exercises. If you’re stepping into cybersecurity from any background, this guide equips you to think strategically about defense without drowning in jargon or overwhelming detail.
Business Wire, a respected authority in tech publishing, highlights this book as a seminal work in understanding deeply embedded malware threats. Their recognition carries weight for anyone serious about cyber security, especially given the increasing sophistication of boot-level attacks. They describe it as '[A] seminal book that explains how to understand and counter sophisticated, advanced threats buried deep in a machine’s boot process or UEFI firmware.' This endorsement underscores the book’s value in shifting perspectives on malware persistence and offers you a pathway to mastering these hidden threats.
“[A] seminal book that explains how to understand and counter sophisticated, advanced threats buried deep in a machine’s boot process or UEFI firmware.” (from Amazon)
Alex Matrosov, Eugene Rodionov, Sergey Bratus(you?)·
About the Author
Alex Matrosov is a leading offensive security researcher at NVIDIA. He has more than two decades of experience with reverse engineering, advanced malware analysis, firmware security, and exploitation techniques. Before joining NVIDIA, Alex served as Principal Security Researcher at Intel Security Center of Excellence (SeCoE), spent more than six years in the Intel Advanced Threat Research team, and was Senior Security Researcher at ESET. Alex has authored and co-authored numerous research papers and is a frequent speaker at security conferences, including REcon, ZeroNights, Black Hat, DEFCON, and others. Alex received an award from Hex-Rays for his open source plug-in HexRaysCodeXplorer, supported since 2013 by the team at REhint.
Alex Matrosov, with over twenty years of deep experience in malware research and firmware security, co-authored this book to expose the hidden complexity of modern persistent threats. You’ll learn how Windows boots, including 32-bit, 64-bit, and UEFI modes, and gain insight into vulnerabilities within these processes. The book walks you through analyzing notorious rootkits like TDL3 and Festi, using tools such as IDA Pro and VMware Workstation to reverse engineer malware and understand its delivery. If you're involved in cybersecurity or malware analysis, this book provides a detailed look at the underexplored area of boot-level threats and forensic techniques that most general resources overlook.
This AI-created book on cyber defense is written to match your background, skill level, and specific goals. You share which areas of cyber security you want to focus on and your experience, and the book is created to guide you through a personalized month-long learning path. It’s designed to help you build relevant skills through daily actionable steps, making complex topics manageable and aligned with your priorities.
TailoredRead AI creates personalized nonfiction books that adapt to your unique background, goals, and interests. Instead of reading generic content, you get a custom book written specifically for your profession, experience level, and learning objectives. Whether you're a beginner looking for fundamentals or an expert seeking advanced insights, TailoredRead crafts a book that speaks directly to you. Learn more.
This tailored book explores a focused, step-by-step journey to fast-track your cyber security capabilities within just one month. It covers essential concepts, practical exercises, and critical knowledge areas that align with your background and specific goals. Through a personalized approach, the book reveals how to build foundational skills and apply daily action steps to develop a strong cyber defense system rapidly. It examines core topics such as threat detection, risk assessment, vulnerability management, and incident response, all tailored to match your interests and experience level. By concentrating on your priorities, this book helps you navigate complex security principles in an accessible, efficient way.
Best for cybersecurity strategists and threat analysts
Kindle version available
Tim Rains is an internationally recognized cybersecurity executive, currently Vice President Trust & Cyber Risk at T-Mobile, with prior leadership roles at Amazon Web Services and Microsoft. His extensive experience advising both public and private organizations underpins this book, which distills his expertise into practical strategies for understanding and combating modern cybersecurity threats. Drawing on his background as a global security leader, Rains offers you insights into the evolving landscape of malware, threat intelligence, and governance, making this a resource grounded in real-world challenges and high-level strategy.
Tim Rains is an internationally recognized cybersecurity executive, advisor, and author. Currently, Tim is Vice President Trust & Cyber Risk at T-Mobile where he leads risk, strategy, assurance, compliance, and vulnerability management. Prior to this, Tim was the Global Security Lead for Worldwide Public Sector at Amazon Web Services. Tim also held the post of Executive Director Cybersecurity Strategy at the Las Vegas Sands Corporation, the world’s largest gaming company. Tim spent 17 years at Microsoft where he worked in numerous roles including Global Chief Security Advisor, Director of Trustworthy Computing, and Technical Lead of Microsoft’s customer-facing Security Incident Response Team.
When Tim Rains, with decades of experience from Microsoft to Amazon Web Services, wrote this book, he aimed to equip you with a nuanced understanding of cybersecurity threats and defenses. You’ll explore detailed analyses of malware evolution, vulnerability trends, and government roles in cyber risk, along with strategic frameworks like Zero Trust and the Intrusion Kill Chain. The book offers a pragmatic look at measuring your organization's cybersecurity effectiveness and how cloud environments reshape security paradigms. This is best suited for cybersecurity professionals and leaders seeking to deepen their grasp of modern threat landscapes and to sharpen their strategic response capabilities.
Ian Neil is a globally recognized Security+ trainer with over 23 years of experience, including designing courses for the US Army in Europe and training Microsoft staff. His ability to break down complex cybersecurity concepts into manageable lessons stems from his extensive certifications and hands-on teaching background. This guide reflects his expertise, offering you a thorough pathway to master the SY0-701 exam objectives and build strong foundational skills for a cybersecurity career.
Ian Neil is one of the world's top trainers of Security+. He is able to break down information into manageable chunks so that people with no background knowledge can gain the skills required to become certified. He has recently worked for the US Army in Europe and designed a Security+ course that catered to people from all backgrounds (not just IT professionals), with an extremely successful pass rate. He is an MCT, MCSE, A+, Network+, Security+, CASP, and RESILIA practitioner that has worked with high-end training providers over the past 23 years and was one of the first technical trainers to train Microsoft internal staff when they opened their Bucharest Office in 2006.
After two decades training diverse learners, Ian Neil crafted this guide to make cybersecurity accessible to everyone, regardless of background. You’ll get detailed coverage of the latest CompTIA Security+ SY0-701 exam objectives, with chapters that unravel security controls, threat actors, cryptographic solutions, and mitigation techniques. The book’s structure, combined with interactive online tools like mock exams and flashcards, helps build your practical understanding of enterprise security and risk management. Whether you’re aiming to pass the exam on your first try or strengthen your security fundamentals for a career shift, you’ll find clear explanations and hands-on strategies tailored for both newcomers and those refreshing their skills.
James Forshaw is a renowned computer security researcher at Google Project Zero and the creator of the network protocol analysis tool Canape. His discovery of complex design issues in Microsoft Windows earned him the top bug bounty of $100,000 and placed him as the #1 researcher on the published list from Microsoft Security Response Center (MSRC). He’s been invited to present his novel security research at global security conferences such as BlackHat, CanSecWest, and Chaos Computer Congress. This impressive background underpins his authoritative guide to network protocol vulnerabilities and exploitation.
James Forshaw is a renowned computer security researcher at Google Project Zero and the creator of the network protocol analysis tool Canape. His discovery of complex design issues in Microsoft Windows earned him the top bug bounty of $100,000 and placed him as the #1 researcher on the published list from Microsoft Security Response Center (MSRC). He’s been invited to present his novel security research at global security conferences such as BlackHat, CanSecWest, and Chaos Computer Congress.
What happens when deep expertise meets network protocol security? James Forshaw, a leading security researcher at Google Project Zero known for his $100,000 Microsoft bug bounty, offers a methodical exploration of network protocols from an attacker’s viewpoint. You’ll gain hands-on skills in capturing, manipulating, and replaying packets, alongside learning how to develop custom tools for dissecting network traffic and reverse-engineering protocol code. The book delves into vulnerability discovery, including memory corruption and authentication bypasses, using tools like Wireshark and custom proxies. If you're involved in penetration testing or network development, this book equips you with a sharp, practical understanding of protocol exploitation and defense.
Rick C. Worley, a seasoned expert in the realm of technology, is an accomplished author renowned for his comprehensive works in the field of computer networking and cybersecurity. With a passion for simplifying complex concepts, Worley has dedicated his career to making the intricate world of technology accessible to individuals at all skill levels, which is evident throughout this guide.
Rick C. Worley, a seasoned expert in the realm of technology, is an accomplished author renowned for his comprehensive works in the field of computer networking and cybersecurity. With a passion for simplifying complex concepts, Worley has dedicated his career to making the intricate world of technology accessible to individuals at all skill levels.
Rick C. Worley, a seasoned expert in technology and cybersecurity, wrote this book to make complex security concepts accessible to a broad audience. You’ll learn how to develop a comprehensive cybersecurity plan that covers network security, threat detection, and incident response, alongside hands-on exercises to build practical skills. The book breaks down essentials like securing mobile and web applications and leading your first security team, making it especially useful for IT professionals, programmers, and students aiming to deepen their security expertise. Whether you’re building foundational knowledge or managing real-world threats, this guide offers a solid framework without overcomplicating the subject.
Building a Career in Cybersecurity offers a strategic approach to launching and advancing your professional path in one of the fastest growing technology fields. Yuri Diogenes, with his extensive experience at Microsoft and as a cybersecurity professor, lays out a clear framework focused on mindset, planning, and essential soft skills rather than just technical details. This book is designed to help you identify your strengths, fill skill gaps, and navigate the often confusing job market with confidence. Anyone seeking to enter or progress in cybersecurity will find this guide a practical companion for building a sustainable, rewarding career.
Yuri Diogenes brings firsthand experience from Microsoft and academia to guide your cybersecurity career journey beyond technical know-how. This book zeroes in on crucial strategies like personal planning, mindset, and soft skills that often determine success in the field. For example, you’ll find actionable advice on building a cloud-based lab to sharpen skills and crafting a career game plan tailored to your goals. If you’re transitioning into cybersecurity or aiming to advance within it, this book offers a realistic roadmap shaped by an insider’s perspective on hiring and industry expectations.
The best Cyber Security books and more, in your inbox each week. No account needed.
Conclusion
These 10 books weave together a tapestry of cyber security knowledge covering everything from hands-on hacking skills to strategic leadership and career development. If you're navigating threats in IoT, start with Practical IoT Hacking to grasp device vulnerabilities. For those seeking actionable defense tactics, Penetration Testing alongside Attacking Network Protocols offers practical tools. Meanwhile, Building a Career in Cybersecurity guides you through the professional landscape.
Pairing The Art of Invisibility with Cybersecurity Threats, Malware Trends, and Strategies provides both personal privacy techniques and a broad understanding of threat evolution. For certification seekers, the CompTIA Security+ SY0-701 Certification Guide lays a solid foundation.
Alternatively, you can create a personalized Cyber Security book to bridge the gap between general principles and your specific situation. These books can help you accelerate your learning journey and sharpen your defenses in a complex digital world.
Frequently Asked Questions
I'm overwhelmed by choice – which book should I start with?
Start with How Cybersecurity Really Works if you're new—it breaks down basics with practical examples. If you're more hands-on, Penetration Testing offers real-world hacking techniques to build solid skills.
Are these books too advanced for someone new to Cyber Security?
Not at all. Several books like How Cybersecurity Really Works and the CompTIA Security+ Guide are designed to ease beginners into the field with clear, accessible lessons.
Which books focus more on theory vs. practical application?
Cybersecurity Threats, Malware Trends, and Strategies leans toward strategic theory, while Practical IoT Hacking and Penetration Testing emphasize hands-on skills and real-world attacks.
Are any of these books outdated given how fast Cyber Security changes?
Most books here are recent and updated, like the 2023 edition of Cybersecurity Threats, Malware Trends, and Strategies. Still, always supplement with current resources and news.
How long will it take me to get through these books?
Reading time varies, but expect 2-4 weeks per book if dedicating focused time. Combining study with hands-on practice, especially for technical books, deepens learning.
Can I get a Cyber Security book tailored specifically to my goals and experience?
Yes! While these books offer solid foundations, a personalized Cyber Security book can tailor insights and strategies to your background and objectives. Try creating your own tailored book for focused, actionable guidance.
📚 Love this book list?
Help fellow book lovers discover great books, share this curated list with others!